DNSSEC
DNSSEC signing that you can see and roll over.
Patchvia DNS signs zones online, as each answer is served, so there is no separate signing step to schedule. Keys and the DS records for your registrar are managed from the zone settings page.
Online signing
Turn signing on for a zone and the server creates its keys and signs the answers it serves. The zone list marks signed zones, and the settings page shows the signing status.
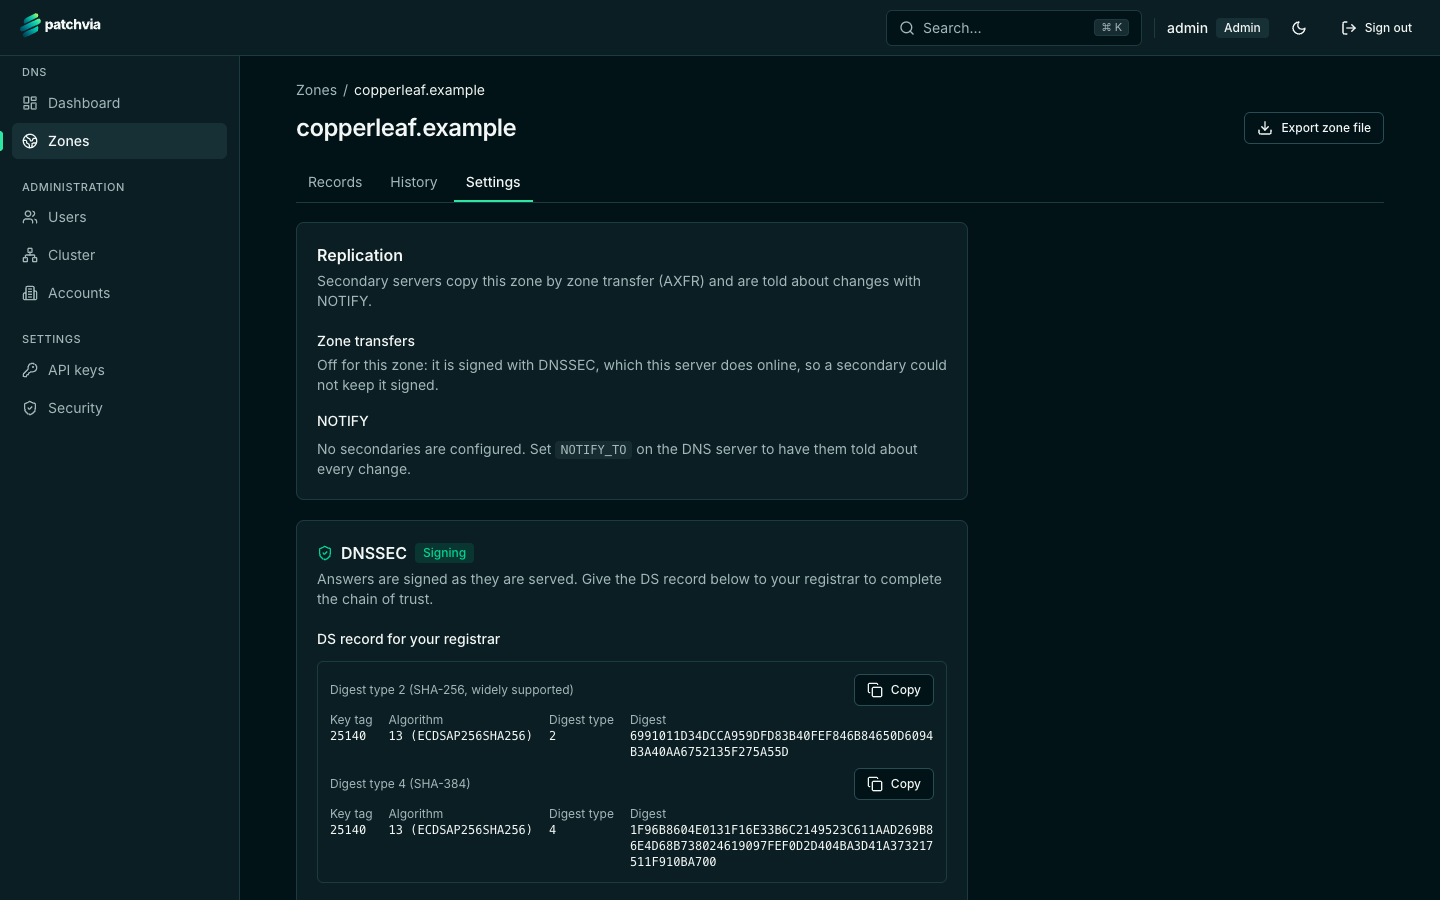
DS records for your registrar
The DS record is what links your zone into the chain of trust. The console shows it with each digest type, so you can copy the one your registrar accepts.
Key rollover
Add a new key, publish it, and give the new DS record to your registrar. Keep the old key until the registrar has the new DS record and the old one is no longer cached. Keys can be marked active or published from the same page.
Where the keys live
DNSSEC private keys are stored in the server’s database, next to password hashes and cluster state. Back up that database like a secret. Losing it means losing the signing keys.
Current limits
NSEC3 is not supported, so denial of existence uses NSEC. TSIG is not supported. DS records for delegated child zones are not managed by the server yet.
Sign your first zone
Turn on signing for a test zone and check the DS record with your registrar’s tools before you change anything live.